Preparing for Quantum Security: An Essential Step for Modern Institutions
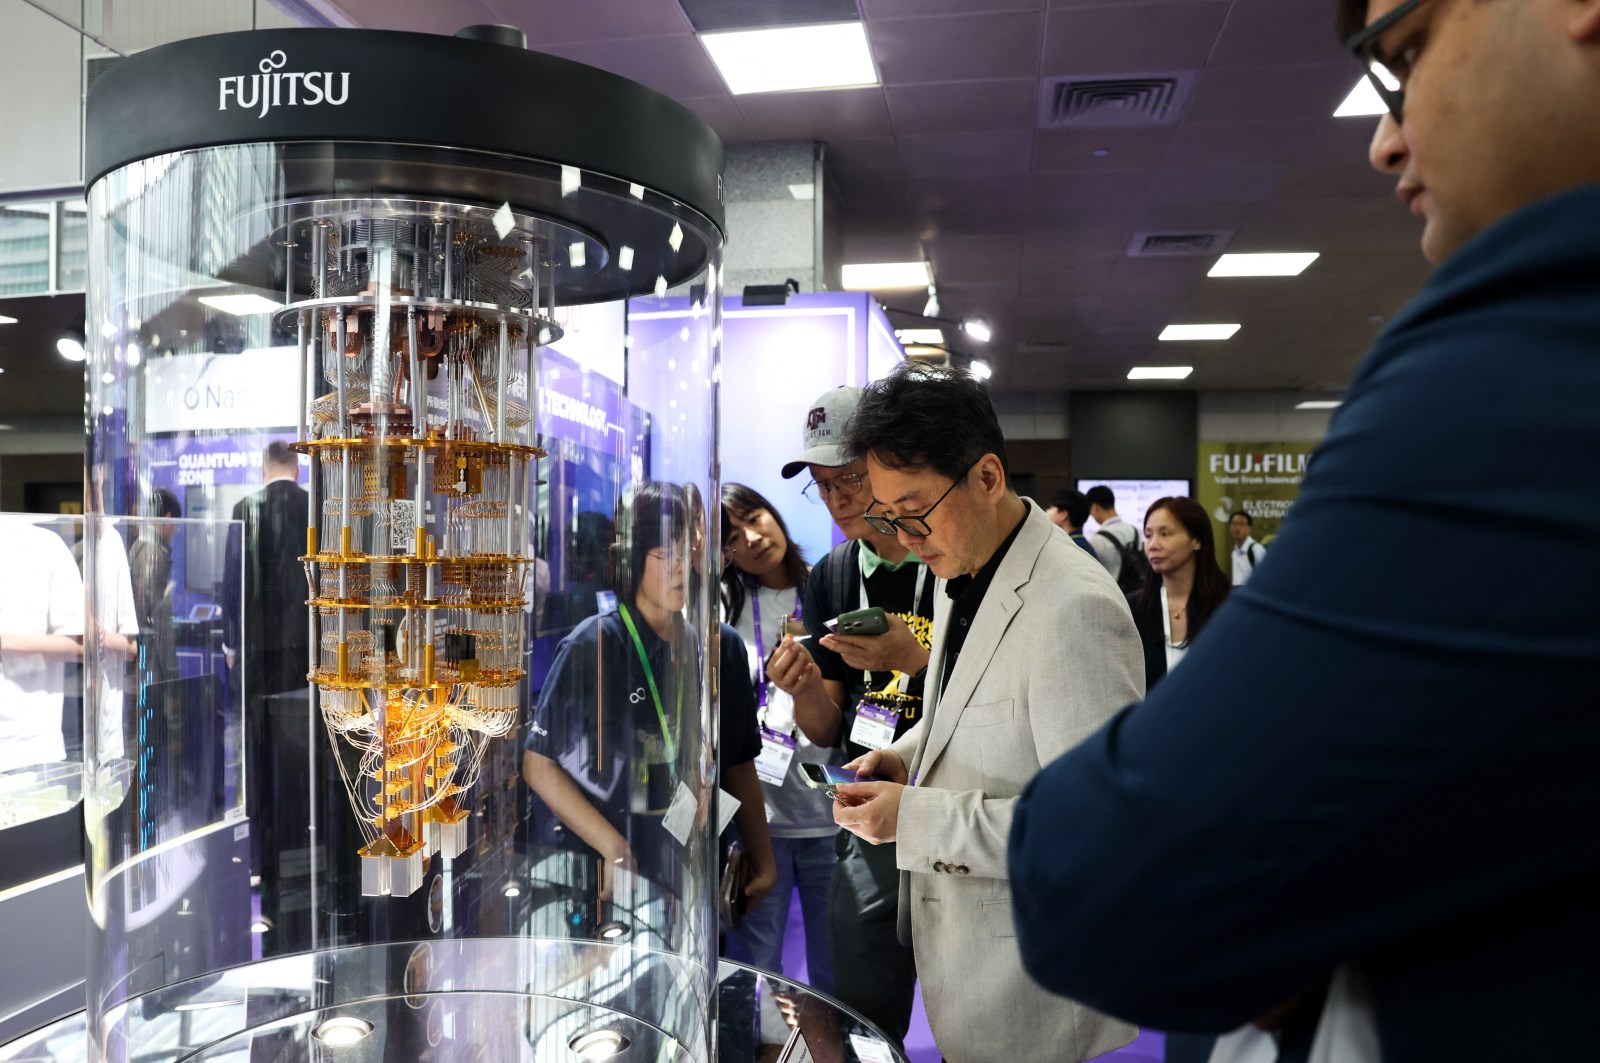
Quantum security has shifted from a theoretical concept to a practical infrastructure challenge. Companies can no longer treat quantum risk as a distant concern; it is now integral to shaping today’s infrastructure decisions. Banking institutions, payment processors, cloud service providers, and digital asset platforms rely heavily on cryptography to secure money, identities, communications, approvals, and transaction flows. The transition to a quantum-safe encryption is crucial and should commence early due to its technical and operational complexity.
The threat posed by quantum computing is straightforward. Quantum computers with sufficient power could eventually compromise the public-key cryptographic systems safeguarding digital signatures, encrypted communications, identity systems, and financial transactions. Institutions handling high-value assets must upgrade to quantum-safe encryption techniques, a process that is often challenging.
The roadmap to achieving quantum security is still unclear. Companies face pressure to prepare for quantum risk even before the market has fully defined what quantum-safe infrastructure entails. Standards are emerging, yet many implementation details remain unresolved, prompting uncertainty for company executives.
Investing in quantum security grants a competitive advantage by allowing institutions to undertake one of the most complex infrastructure migrations of the next decade. Early experimentation provides time to understand cryptographic dependencies, test new architectures, build internal expertise, and avoid rushed decisions.
Why Early Experimentation is Vital
Large organizations often lack a comprehensive understanding of cryptography within their infrastructure. Identifying encryption systems, key-management flows, vendor dependencies, and legacy systems is essential for achieving quantum security. While this task may seem basic, it is anything but simple for institutions with extensive software, vendor relations, and operational workarounds.
Early movers can answer critical questions: Which systems rely on algorithms vulnerable to quantum computing? What protects high-value assets or sensitive data over long periods? Which systems can be upgraded without significant disruption? The inventory created from these efforts becomes a valuable strategic asset, helping prioritize systems needing immediate attention.
Testing and Development Insights
The U.S. National Institute of Standards and Technology (NIST) has played a pivotal role in evaluating post-quantum cryptographic algorithms, providing benchmarks for credible algorithms ready for testing and deployment. While NIST ensures standards, institutions must still understand and test how quantum-safe encryption functions within real systems, considering constraints like transaction size, latency, cost, and auditability.
These considerations are crucial for institutions using distributed signing and MPC-based custody. Quantum-safe migration must accommodate systems where cryptographic keys are divided among multiple parties, reducing single points of failure. Introducing post-quantum signatures poses questions regarding transaction performance and the integrity of distributed approval workflows, demanding thorough testing and practical experimentation.
Benefits of Gradual Migration
Security migrations go beyond simple software updates; they necessitate comprehensive testing, audits, customer communication, and governance approvals. Companies starting early can test hybrid architectures and phase upgrades into product roadmaps, often running classical and post-quantum systems in parallel. This phased approach allows for calculated decisions without immense pressure.
The alternate scenario is replacing critical security infrastructure during a crisis or under regulatory scrutiny. Institutions that cannot afford downtime or ambiguous key control must avoid procrastination. Beginning early ensures greater control over migration processes.
Market Recognition and Early Adoption
Security has become a key element in commercial due diligence. Enterprises, financial institutions, and infrastructure partners are increasingly required to demonstrate operational risk management, making quantum risk part of such conversations due to its impact on identity systems, transaction approval, and data protection.
Companies capable of articulating a quantum-readiness plan and showing evidence of testing NIST-standardized algorithms gain an advantage in enterprise sales and institutional partnerships. Clear evidence of preparation appeals to customers seeking assurance of forward-thinking infrastructure providers.
Moreover, early adopters often set industry standards in emerging infrastructure shifts. Experimentation helps define acceptable practices regarding migration timelines, hybrid deployment, risk governance, and vendor requirements.
Examples of Institutions Already Taking Action
Several major financial institutions and technology companies are actively testing quantum-safe infrastructure:
- HSBC piloted quantum-secure technology for tokenized physical gold transactions, emphasizing protection from potential quantum attacks.
- JPMorgan Chase is developing quantum-safe digital signature capabilities for financial purposes, with a focus on authentication and access security.
- Google, integrating post-quantum capabilities into its core infrastructure, announced quantum-safe digital signatures in Cloud KMS.
These initiatives, although preliminary, indicate a proactive approach where serious institutions are preparing their infrastructure for impending transformations. Quantum readiness demands sustained testing and a profound comprehension of how cryptography supports modern financial and digital infrastructure.