Recent Disruptions Highlight the Need for Accountability in System Changes
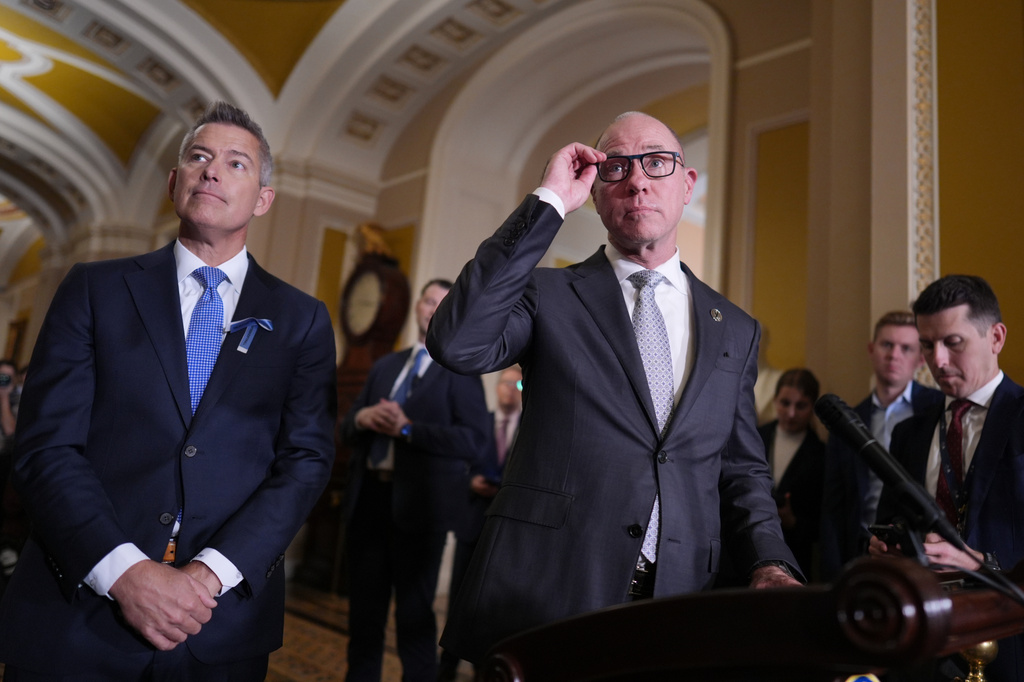
Transportation Secretary Sean Duffy listened as FAA Administrator Bryan Bedford addressed reporters at the U.S. Capitol. The discussion centered around a series of recent disruptions affecting various systems heavily relied upon by Americans.
Within a span of five days, Microsoft 365, the Federal Aviation Administration, and Chase banking experienced significant outages. These events interrupted email services, halted nationwide air travel, and blocked banking transactions, respectively. Notably, none of these outages are currently linked to cyberattacks.
According to official statements, Microsoft found no evidence of an attack, Chase’s issues were not cyber-related, and the FAA cited no signs of cyber intrusion. A remote radio site where a contractor was working has been identified as a potential source of the FAA’s issues, but investigations continue.
Federal officials confirm no connections among the outages or any external interference, which raises significant concerns about internal systems management. Organizations have invested heavily in cybersecurity to protect against external threats. These incidents, however, underscore a different risk: internal technical procedures.
“The danger may not have been a sophisticated attacker — it may have been merely a routine upgrade,” observed Vincent E. Bianco III, an experienced FAA veteran.
Bianco spent 23 years in FAA air traffic control and emphasized the importance of rigorous safety risk management. He pointed out that successful organizations assess changes thoroughly before implementation, whereas failures often occur when responsibility is unclear.
The FAA disclosed that a contractor was working on deploying a new router at a remote site, which is under investigation. Microsoft admitted to trouble caused by a recent network capacity upgrade, highlighting a latent defect. Chase cited a software bug, though details remain scant.
Bianco argues that management should take ownership of maintenance decisions, not just rely on technology. He emphasizes the necessity for management to question the timing of maintenance, rollback plans, and dependencies.
Aviation has long understood the need for management oversight. The FAA’s latest directives require a management official to sign off on any planned change, ensuring accountability is documented. Similar practices are advised for the banking sector.
The term “routine” emerges as particularly dangerous. Routine procedures often bypass scrutiny due to past successes, but as Bianco notes, “The hundred-and-first is the one that makes the front page of the newspapers.”
The FAA has not clarified whether the Nov. 13 router replacement followed their change management orders. It remains to be seen if accountability was properly managed prior to the event, as congressional oversight is expected to demand answers.
The same inquiries should be extended to Microsoft and Chase. Understanding what changes were made, who approved them, and what testing was conducted is crucial for future safety and reliability.
In conclusion, Bianco stresses that increasing budgets or changing vendors are insufficient solutions. True improvement comes from holding individuals accountable for the outcomes of system changes.