Florida Man Indicted for Ransomware Fraud Scheme
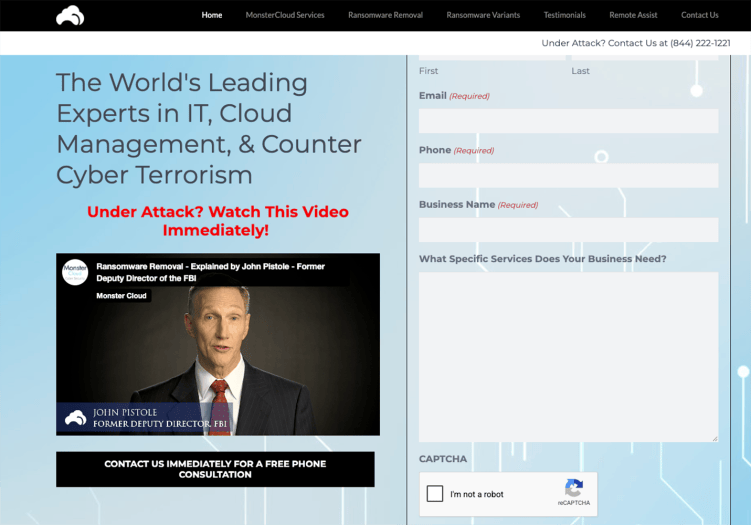
Zohar Pinhasi, a Florida man previously investigated by ProPublica in 2019, was indicted on federal charges for defrauding clients of his ransomware data recovery firm. The Department of Justice reports that Pinhasi promised clients he could recover encrypted files without paying hackers. In reality, he paid the ransom and charged clients more.
ProPublica’s 2019 article, “The Trade Secret,” had already highlighted this scheme. The investigation revealed that victims were harmed twice: first, by hackers who encrypted their files and demanded ransom, and second, by Pinhasi’s firm, MonsterCloud, which falsely claimed not to pay ransoms.
By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself,said U.S. Attorney Joseph Nocella in a press release on October 7.
Ransomware was becoming a major cyberthreat when ProPublica published its findings. Hackers targeted data from governments, schools, and businesses, demanding ransom often paid in cryptocurrency. The report focused on how firms like MonsterCloud and insurance companies contributed to the extortion cycle.
Today, ransomware remains a prevalent threat. The danger to national security has increased with reports suggesting hostile foreign governments use ransomware for espionage. The rise of AI tools is also making it easier for attackers to distribute ransomware.
Pinhasi, also known as Zack Green, told ProPublica in 2019 that MonsterCloud did not guarantee data recovery by any specific method. “How we do it, it’s our problem,” he stated. He referred to the methods as a “trade secret.”
Attempts to reach Pinhasi or secure comments from his attorney were unsuccessful. The U.S. Attorney’s Office stated that Pinhasi pleaded not guilty to the federal charges.
ProPublica’s investigation included interviews with MonsterCloud’s clients and ransomware experts. Findings indicated that MonsterCloud likely paid ransoms for clients. Many law enforcement agencies used MonsterCloud, believing they did not pay ransoms, a practice they sought to avoid.
Pinhasi, a self-described former Israeli military IT security officer, managed MonsterCloud, which handled up to 30 calls daily and employed around 20 people. Federal investigators claim Pinhasi charged clients over $19 million and made ransom payments exceeding $8 million. In one instance, he paid a ransom of about $8,200 but charged the client roughly $150,000.
If convicted, Pinhasi could face up to 20 years in prison. An FBI official expressed disappointment over Pinhasi’s actions, emphasizing that such deception is intolerable.
The Justice Department did not comment on ProPublica’s findings that an FBI associate was linked to MonsterCloud. John Pistole, once an FBI deputy director, was in a promotional video for MonsterCloud, highlighting its role in data recovery and protection. Pistole was not mentioned in Pinhasi’s indictment.
Pinhasi promoted MonsterCloud’s law enforcement ties as a sign of its integrity. Despite multiple attempts, Pistole and associated authorities did not respond to requests for comment regarding his connection to MonsterCloud.
In past statements, Pistole acknowledged that ransom payments were common practice in cases like MonsterCloud’s. This business model, as understood by Pistole, involved paying ransoms and facilitating best practices for future protection.